Sunbytes CyberCheck
Are we secure?
Get a defensible security baseline and a clear 30/60/90-day roadmap in 3–4 weeks with Sunbytes CyberCheck.
CyberCheck is for teams that need one defensible baseline
Use CyberCheck when you need to answer security questions, show evidence, and decide what to fix first before choosing a longer security path.

Questionnaires rely on guesswork
Your team can answer some buyer questions, but the evidence behind each answer is scattered or inconsistent.Evidence is hard to show
Policies, screenshots, access records, and security notes exist in different places, with no reusable evidence checklist.Priorities are unclear
Vulnerability items, process gaps, and ownership issues compete for attention. The team needs a ranked view, not more noise.Next step is not obvious
You are not ready to commit to a framework-specific readiness track or continuous partnership until the baseline is visible.

What CyberCheck produces

Baseline snapshot
A structured view of your current posture across 18 security domains, showing what is in place, what is missing, and what needs validation.

Prioritised roadmap
A practical 30/60/90-day plan that ranks findings by risk, effort, dependency, and business impact — so your team knows what to fix first.

Evidence checklist
A reusable checklist of proof points, gaps, owners, and next actions for buyer questionnaires, leadership updates, and follow-up security work.
How CyberCheck works
Fixed price after scope confirmation. Built for lean teams. Designed to minimise disruption while producing usable evidence.
| Stage | What happens | Output |
|---|---|---|
| 1. Kickoff & scope | Align on business context, systems in scope, current evidence, and the pressure behind the request. | Agreed scope, timeline, evidence request list, and working plan. |
| 2. Review & validate | Review provided evidence, validate what exists, identify gaps, and clarify unclear ownership with key stakeholders. | Findings by domain, evidence notes, risk observations, and open questions. |
| 3. Report & roadmap | Turn findings into a prioritised roadmap and walk stakeholders through what to fix, prove, or defer. | Baseline report, 30/60/90-day roadmap, evidence checklist, and executive summary. |
What we cover across
18 security domains
CyberCheck gives you a broad security posture view — from governance and access to technical controls, data protection, and resilience readiness.
– Governance & Policies: Ownership, direction, documentation, and decision records.
– Risk Management: How risks are identified, prioritised, tracked, and reviewed.
– Asset & Inventory Management: Visibility of systems, data, services, devices, and ownership.
– Security Awareness: Training, user awareness, and human-risk reduction basics.
– Third-Party & Vendor Risk: Supplier visibility, due diligence, and recurring vendor review basics
– Endpoint Security: Device hygiene, endpoint protection, hardening, and ownership.
– Network Security: Exposure control, segmentation, remote access, and network visibility.
-Secure Configuration & Hardening: Baseline configurations and review practices for critical systems.
– Vulnerability Management: How findings are discovered, prioritised, assigned, remediated, and tracked.
– Logging & Monitoring: Visibility, alerting, audit trails, and monitoring ownership.
– Application Security: Secure SDLC checkpoints, dependency risk, review practices, and release readiness.
– Identity & Access Management: Access control, MFA, joiner/mover/leaver basics, and role alignment
– Privileged Access: Admin boundaries, elevated permissions, accountability, and review practices.
– Change & Release Management: Controlled, traceable changes across systems, code, configuration, and releases.
– Data protection & privacy: Data handling, retention, confidentiality, and privacy-by-design practices.
– Backup & recovery: Backup coverage, restore testing, recovery ownership, and documentation.
– Incident response: Incident roles, escalation, evidence capture, and post-incident follow-up.
– Business continuity: Continuity planning, critical service recovery, and resilience expectations.
What your team can answer after CyberCheck
-
Faster security
responsesAnswer customer questionnaires with consistent wording and reusable proof points instead of restarting the evidence search each time.
-
Clear remediation
prioritiesKnow what to fix first, what can wait, and why — with owners and next steps visible to technical and non-technical stakeholders.
-
One shared
risk viewGive leadership, delivery, and customer-facing teams the same view of current posture, priority gaps, and planned next actions.


Start with a clear security baseline
Where CyberCheck fits
Compare CyberCheck, Compliance Readiness, and CyberCare based on your current security needs.
| CyberCheck | Readiness | CyberCare | |
|---|---|---|---|
| Best fit | You need a first baseline and priorities. | You have a target framework or audit pressure. | You need ongoing security ownership. |
| Primary question | Are we secure? | Are we ready for this framework? | Can we stay secure over time? |
| Scope | 18-domain posture baseline. | Framework-specific gap and evidence readiness. | Recurring security cycle and follow-through. |
| Main output | Baseline report, 30/60/90 roadmap, evidence checklist. | Control map, remediation plan, audit-facing artifacts. | Priority tracking, progress updates, evidence upkeep. |
| Commercial model | Fixed price after scope confirmation. | Scoped readiness engagement. | Ongoing partnership cadence. |
| What it is not | Not a pentest, scan, or certification audit. | Not a certification body. | Not a one-off report. |
| Next step | Start your CyberCheck assessment. | Book a Compliance Readiness call. | Explore CyberCare. |
Our verified credentials
Why teams choose Sunbytes
A Netherlands-led partner for evidence-based security work: clear scope, controlled handling, and practical next steps after the baseline.
Baseline before commitment
CyberCheck gives lean teams a first security baseline before they choose remediation, compliance readiness, or a continuous partnership.
Evidence-led from the start
Findings are connected to proof points, gaps, owners, and next actions — so the report can support real buyer and leadership conversations.
Controlled information handling
Access and information handling operate under Sunbytes’ ISO 27001-certified ISMS, with controlled sharing and audit-conscious practices.
Roadmap, not scare tactics
The 30/60/90-day roadmap shows what to fix first, what can wait, and what requires deeper validation through a separate service.
Netherlands-led security expectations
Sunbytes works with European stakeholders who expect direct communication, defensible evidence, and practical ownership of next steps.
Clear path after CyberCheck
If the baseline shows a specific need, the next step can move into Compliance Readiness, CyberCare, or a plug-in security service without restarting context.
Evidence-backed security work, grounded in delivery experience
CyberCheck is delivered by a Sunbytes team used to working with international stakeholders, controlled information handling, and practical security evidence.
-
15+
Years of experience -
300+
Projects delivered -
20+
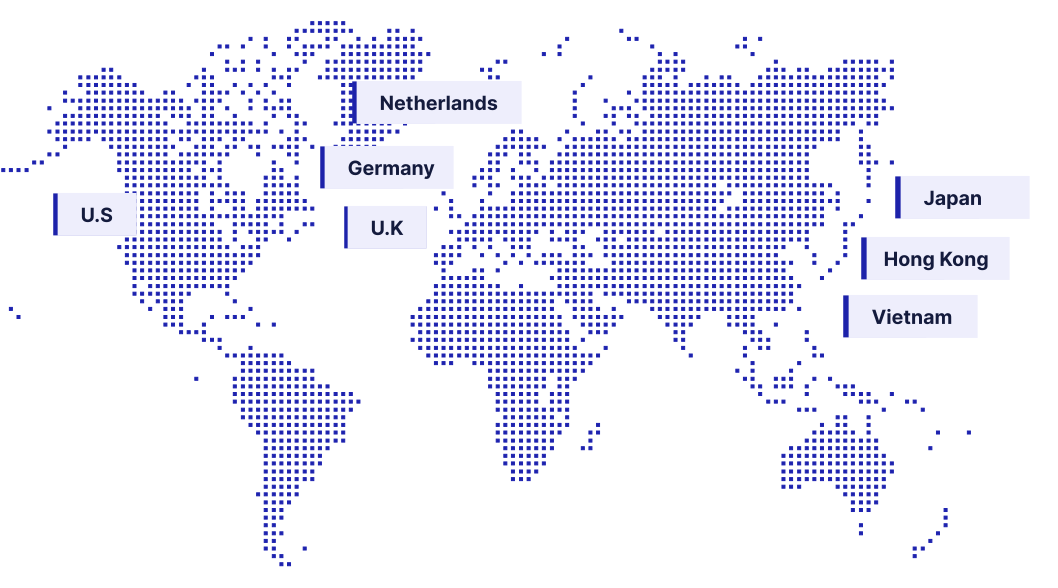
Countries
Testimonials
“Sunbytes started to assemble the team at their own risk even before we had our seed investment signed. When that happened we could make a flying start.”

“We were impressed by the vulnerabilities that were discovered. We can tell that the pentesters dug deep to discover the vulnerabilities, and not just a surface scan.”
“Sunbytes’ thorough approach uncovered risks we’d never even considered and opened my eyes to just how important it is to secure our platform from day one.”
“Sunbytes provided practical, prioritized remediation guidance that our team could act on immediately.”
Update the latest cybersecurity trends from Sunbytes
- Cybersecurity
DevSecOps and NIS2: what Dutch companies must do before July 2026
DevSecOps NIS2 readiness means proving that your software development process has working security controls, not just written policies. Before July 2026, Dutch companies in scope for the Cyberbeveiligingswet need evidence for Article 21 controls such as secure development, supply chain security, access management and effectiveness testing. For engineering teams, the practical evidence usually comes from […]
- Cybersecurity
NIS2 penetration testing requirements: what Article 21(2) compliance looks like
NIS2 penetration testing is not a checkbox exercise. Article 21 does not name one single testing tool that every entity must use. It requires organisations to handle vulnerabilities and assess whether their cybersecurity risk-management measures work in practice. That distinction matters. A vulnerability scan can tell you that a known weakness exists. A DAST scan […]
- Cybersecurity
NIS2 implementation roadmap: a 12-week plan for EU SMEs
A NIS2 implementation roadmap should turn the directive into a sequence your management board, IT team, compliance lead, and suppliers can execute. For most EU SMEs, the work does not fail because Article 21 is unknown. It fails because scope, risk assessment, remediation, evidence, and board approval happen in the wrong order. This 12-week plan […]
Start your CyberCheck assessment
Share your security context, current pressure, and evidence availability. We will confirm the right scope, fixed price, and 3–4 week assessment plan before work begins.