Sunbytes is certified to ISO/IEC 27001:2022
Our certified Information Security Management System provides a consistent framework for managing information security risk across the Sunbytes operations covered by the certification.
That framework supports how we handle information across our workforce solutions (HR operations), cybersecurity solutions, and transformation solutions.
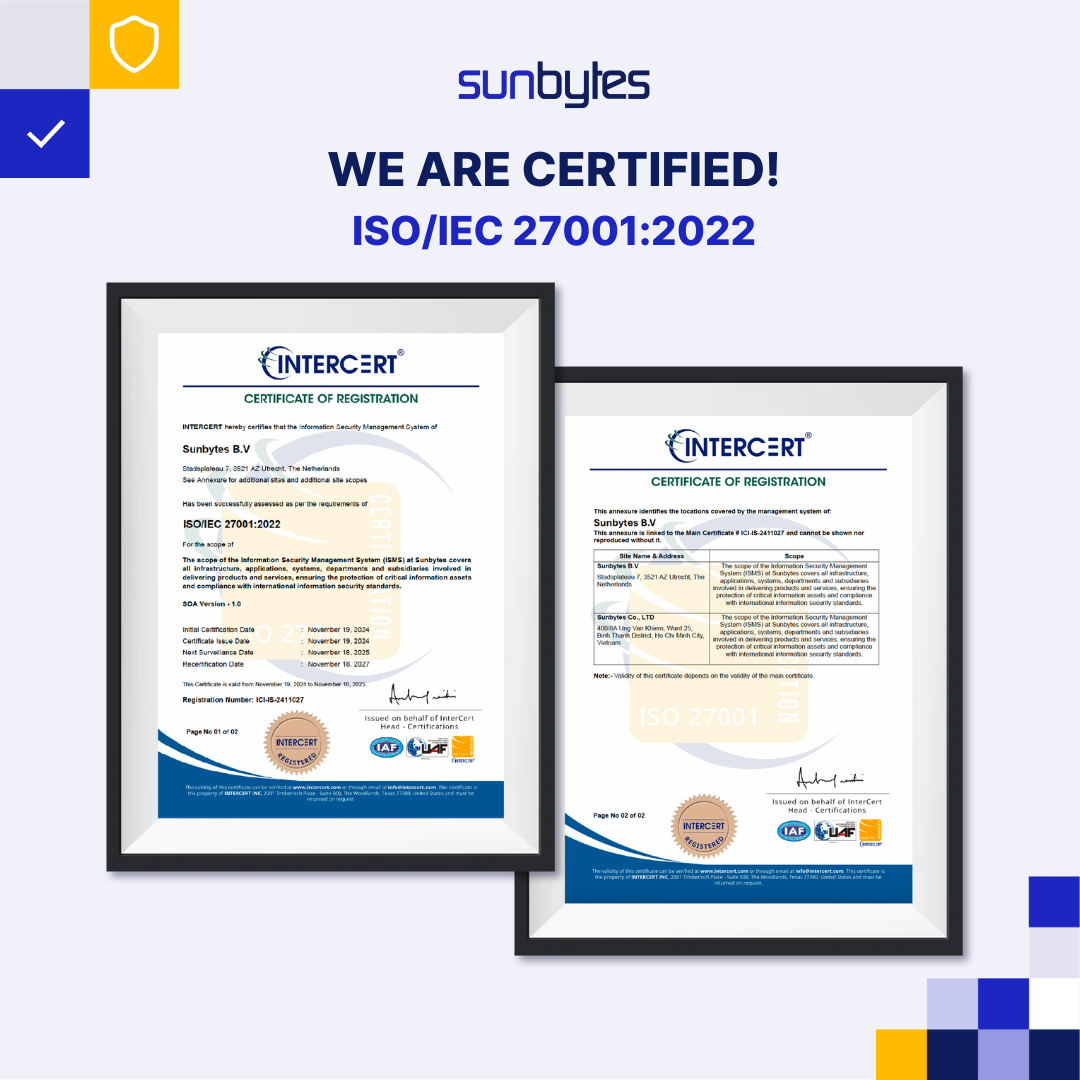
Our ISO/IEC 27001:2022 certification
ISO/IEC 27001 sets the requirements for an Information Security Management System, providing a structured approach to identifying, managing, and reviewing information security risks.
Sunbytes is certified to ISO/IEC 27001:2022.
The certification provides clients and organisations assessing Sunbytes with an independently verified reference for how information security is managed within the certified scope.
– Standard: ISO/IEC 27001:2022
– Registration number: ICI-IS-2411027
– Scope: Sunbytes’ ISMS covers the infrastructure, applications, systems, departments, and subsidiaries involved in delivering its products and services.
What our certification means across our services
Whether Sunbytes is handling workforce information, security findings, or access to digital systems, our certified ISMS provides a consistent framework for managing information security risk.
Workforce solutions
Better control around sensitive people information
Workforce services can involve CVs, employee records, contracts, payroll-related information, and other business data.
Our ISMS provides a defined framework for managing access, responsibilities, and information security risk around that information.

Cybersecurity solutions
Stronger governance around highly sensitive security work
Security engagements can involve credentials, system details, vulnerabilities, test results, and other sensitive technical information.
Our ISMS provides a defined framework for controlling access, managing responsibilities, and handling information security risk throughout the engagement.
Transformation solutions
More disciplined access to code, systems, and environments
Digital delivery can require access to source code, credentials, development environments, project information, and client systems.
Our ISMS provides a consistent framework for managing that access and the related information security responsibilities.
How this relates to client data
ISO/IEC 27001 provides the management framework for information security. It does not replace the contractual, privacy, regulatory, or engagement-specific requirements that may apply to client information.
Where Sunbytes processes or accesses client data, the relevant requirements are defined according to the service, systems, information involved, and applicable contractual or data-processing arrangements.
Organisational framework:
Our certified ISMS defines how information security risks are managed within the certified scope.
Engagement-specific requirements:
Each engagement may require additional controls, responsibilities, or data-handling requirements based on the client, service, and applicable obligations.
Experience behind the standard
Our ISO/IEC 27001 certification sits alongside the broader experience Sunbytes brings to international client engagements.
-
15+ years
Supporting businesses across markets -
20+ countries
Experience working with international organisations -
300+ projects
Across products, platforms, and business operations

Need more information about our security practices?
If your procurement, legal, security, or compliance team is assessing Sunbytes, we can provide the relevant certification information and discuss any engagement-specific requirements.