Secure code review services
Secure code review services for safer releases
Find code-level security risks before release, with findings your developers can fix and prove.
When code review becomes necessary
Secure code review fits when the risk sits inside the source code, not only at the exposed surface.
Before a major release
Selected features handle authentication, authorization, payments, sensitive data, or external APIs.After recurring security findings
Scans or tests keep pointing to issues that need source-level validation and fix guidance.Before buyer security review
Highlight Unique Selling Propositions with a short summary of the key feature and how it benefits customers.When developers need secure coding guidance
Findings must be specific enough to assign, implement, and retest.When inheriting a codebase
Ownership changes, legacy assumptions, or outsourced code need security validation before more work continues.
Code-level risk is hard to prove late
Security review becomes expensive when the first clear finding appears after code is already merged, released, or questioned by a buyer. The issue is not only whether a vulnerability exists. The issue is whether your team can find it, prioritize it, fix it, and show evidence that it was closed.
-

Logic flaws stay hidden
Authorization, data flow, and business-rule mistakes often depend on application context that automated scanning alone cannot fully interpret.
A code-level review follows how sensitive actions and data move through the application, helping identify weaknesses that may look acceptable in isolation but create risk when combined.
-
Release pressure narrows review
When security review happens close to release, teams have less time to investigate findings, understand their impact, and make changes safely.
Reviewing code earlier creates more room to examine risky logic, agree on remediation, and resolve issues before release pressure turns security work into last-minute triage.
-
Findings stall without fix guidance
A finding that only explains what is wrong still leaves developers to determine the right remediation and its priority.
Secure code review should provide enough technical context and recommended next steps for the responsible team to assign, implement, and verify the fix without restarting the investigation themselves.
-
Evidence gets scattered
Tickets, scan exports, pull-request comments, and isolated fixes rarely provide a clear record of what was reviewed and what was resolved.
A structured review brings findings, affected areas, remediation status, and closure evidence together, creating a more useful record for internal security review or later due-diligence discussions.


Need a review plan before release?
What the review checks in the code
| Focus area | What is reviewed | Output |
|---|---|---|
| Access and data flow | Authentication, authorization, role checks, data handling, and encryption patterns in selected code paths. | Validated findings with affected code area, severity, and fix direction. |
| Input and API behavior | Input validation, injection risk, serialization, API boundaries, error handling, and unsafe assumptions. | Developer-ready remediation guidance tied to the application context. |
| Secrets and dependencies | Secrets exposure, package risk, dependency use, repository hygiene, and selected CI/CD security signals. | Prioritized risks that can be assigned, remediated, and retested. |
How the review runs
-
1. Scope
Agree the codebase, language, modules, release context, review depth, and security questions to answer.
-
2. Access
Set up repository snapshot or controlled access, plus documentation needed to understand architecture and data flow.
-
3. Review
Run SAST-supported analysis and manual validation against the scoped application context and relevant OWASP/CWE guidance.
-
4. Report
Deliver validated findings, severity, affected area, impact, remediation guidance, executive summary, and evidence summary.
-
5. Retest
Validate fixes and provide closure evidence where retesting is included in scope.


Review scope
Choose the level of code evidence your release needs.
| Area | Feature | App | Release |
|---|---|---|---|
| Best fit | Critical feature | Selected application | Pre-release check |
| Review focus | Auth, API, data flow | High-risk modules | Change set + core paths |
| Method | SAST + manual | SAST + manual | SAST + manual |
| Deliverables | Findings + fixes | Report + summary | Report + closure evidence |
| Retest | Optional | Optional | Included if scoped |
| Remediation support | Scoped separately | Scoped separately | Scoped separately |
What your team receives

Code-level findings report
Validated findings with affected area, severity, exploit relevance, and practical impact. Findings are prioritized so engineering can decide what to fix first.

Developer-ready fix guidance
Remediation guidance that names the unsafe pattern and the expected correction. The goal is to make findings assignable, not just visible.

Evidence and closure pack
Executive summary, evidence summary, and retest or closure note where scoped. The pack shows what was reviewed, what was fixed, and what remains open.
Our verified credentials
Customer success is our priority
A pentest that went beyond the surface
A new authentication layer needed deeper validation. Sunbytes combined manual and automated grey-box testing to uncover and classify vulnerabilities, then guided the team through the findings and remediation options.
Grey-box pentest · SOC 2 & ISO-aligned reporting · 9 findings classified
From concept to a working prototype in 3 sprints
SandGrain needed to turn its post-quantum authentication concept into a secure, scalable cloud platform without compromising reliability. Sunbytes assembled a seven-person multidisciplinary team and delivered a functional prototype in three sprints.
15 releases · 3,380 test cases · 1,777 automated tests
Six weeks from security testing to launch readiness
Methodemeter was preparing to launch a digital education platform without dedicated in-house security expertise. Sunbytes ran a black-box pentest, guided remediation, and aligned testing with GDPR, NIS2 and ISO 27001.
6-week test-to-fix cycle · GDPR, NIS2, ISO 27001 · Launched clean
Web, API and mobile tested before an IPO security audit
C2C needed its production product tested across web, API, iOS and Android before an IPO security audit. Sunbytes ranked each finding and provided remediation guidance the team could act on.
Web, API, iOS & Android · All identified findings remediated · 5.0 Clutch review
Testimonials
“Sunbytes started to assemble the team at their own risk even before we had our seed investment signed. When that happened we could make a flying start.”

“We were impressed by the vulnerabilities that were discovered. We can tell that the pentesters dug deep to discover the vulnerabilities, and not just a surface scan.”
“Sunbytes’ thorough approach uncovered risks we’d never even considered and opened my eyes to just how important it is to secure our platform from day one.”
“Sunbytes provided practical, prioritized remediation guidance that our team could act on immediately.”
Why teams choose Sunbytes
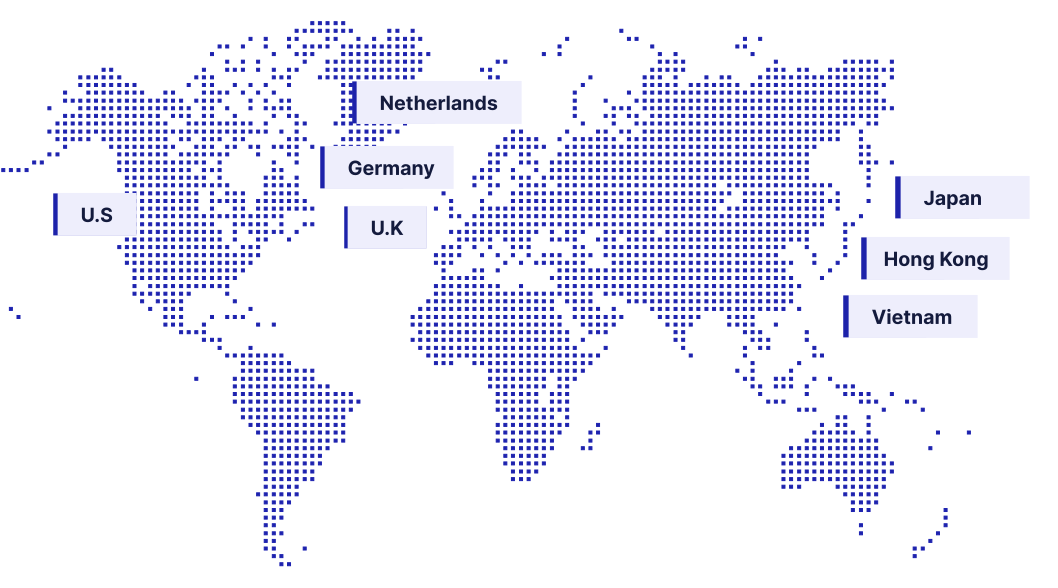
A Netherlands-led partner for code-level security review, controlled access, and remediation-ready evidence.
Review with delivery context
Findings are prioritized by release impact and remediation path, not by scanner output alone.
ISO 27001-certified ISMS
Repository access, secure sharing, and audit trails are handled under Sunbytes information security controls.
Manual validation plus tooling
SAST supports coverage. Manual review validates business logic, data flow, and exploit relevance.
Developer-ready remediation
Reports state what to fix, where it appears, why it matters, and what evidence should close it.
Evidence for buyer reviews
Outputs help answer what was reviewed, what was found, what was fixed, and what remains open.
Remediation support when scoped
If needed, Sunbytes engineering capability can support selected fixes without moving product ownership away from your team.
Secure review work backed by delivery proof
Security review needs controlled access, clear reporting, and delivery discipline. Sunbytes brings that structure across software and security engagements.
-
15+
Years of experience -
300+
Projects delivered -
20+
Countries
Ready to request a code review plan?
Share your application scope, release context, and main security concern. Sunbytes proposes the review scope before any timeline or pricing is discussed.